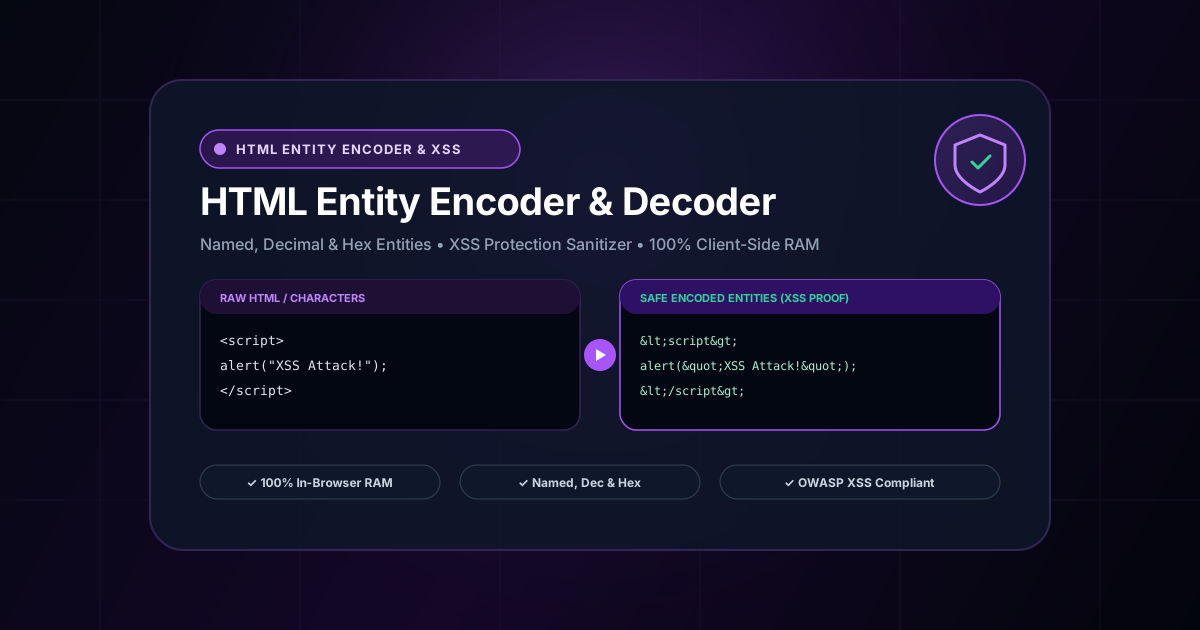
Everything You Need to Know About HTML Entity Encoder & Decoder (XSS Safe)
What is HTML Entity Encoder & Decoder (XSS Safe)? Encode and decode HTML entities bidirectionally. Named, decimal, and hex entities with dedicated OWASP-compliant XSS sanitization and 100% in-browser privacy. Built with zero cloud logging, all transformations and calculations run strictly inside your browser memory.
- Canonical Utility:
- HTML Entity Encoder & Decoder (XSS Safe) on InnoxTools
- Execution Sandbox:
- 100% Client-Side RAM (Zero Cloud Storage)
- Compliance & Standards:
- W3C, RFC Compliant, Air-Gapped Safe
- Runtime & Complexity:
- Local V8 / WebAssembly (O(n) Linear Execution)
- Network Transmission:
- 0 Outbound Telemetry (Offline Capable)
- License & Usage:
- Free Commercial & Personal (Unlimited Runs)
In modern web application development, handling untrusted user input, rendering dynamic content, and preventing security exploits are critical engineering responsibilities. HyperText Markup Language (HTML) reserves specific characters—notably `<` (less-than), `>` (greater-than), `&` (ampersand), `"` (double quote), and `'` (single quote)—to denote the structural syntax of tags, attributes, and entities.
When raw user-submitted text containing these reserved characters is rendered directly into the Document Object Model (DOM) without proper character escaping, web browsers interpret the characters as executable markup. This vulnerability is the root cause of Cross-Site Scripting (XSS)—consistently ranked among the top web application security vulnerabilities by the Open Web Application Security Project (OWASP). Malicious actors exploit unescaped input to inject arbitrary `<script>` tags, steal sensitive session tokens, and hijack user sessions.
Beyond security, developers and content authors routinely encounter typography symbols, foreign language scripts, mathematical notations, and currency signs (such as `©`, `™`, `€`, `£`, `→`, and `≠`) that must be consistently displayed across diverse browsers, email clients, and legacy character sets without encoding corruption (mojibake).
The InnoxTools HTML Entity Encoder & Decoder provides an indispensable, 100% client-side security and formatting studio created by INNO XPERT. It offers instant bidirectional transformation between raw characters and their corresponding Named entities (`<`, `©`), Decimal entities (`<`, `©`), and Hexadecimal code points (`<`, `©`).
Equipped with a dedicated 'Strict XSS Sanitizer' mode adhering to OWASP guidelines, configurable encoding scopes (Dangerous Only, Non-ASCII Unicode, or All Characters), live character telemetry, and 1-click clipboard copying, InnoxTools ensures your web applications, email templates, and markdown documents remain secure, compliant, and beautifully rendered.
How It Works Under the Hood
Select Operation Mode (Encode vs Decode)
Choose 'Encode Entities' to convert unescaped text or HTML markup into safe entities. Choose 'Decode Entities' to restore entity strings back into clean, readable text.
Choose Encoding Format & Security Scope
When encoding, select your desired format: Named entities (`&`), Decimal (`&`), Hexadecimal (`&`), or Strict XSS Sanitizer. Specify the scope to target dangerous HTML characters only, non-ASCII Unicode symbols, or all characters.
Instant In-Memory Transformation
As you type or paste text into the input panel, our client-side lexical engine parses code points in real-time, executing character replacement entirely inside local browser memory.
1-Click Copy or File Download
Click 'Copy' to copy the encoded or decoded output directly to your clipboard, or click 'Download' to save the output as a `.txt` file on your computer.
Key Architectural Capabilities & Features
Bidirectional Encoding & Decoding
Easily switch between converting raw text to HTML entities and decoding entity strings back to readable characters.
4 Encoding Formats
Full support for Named entities, Decimal entities, Hexadecimal entities, and Strict XSS Sanitizer mode.
Granular Scope Filtering
Choose whether to encode Dangerous HTML characters only (`< > & " '`), Non-ASCII Unicode, or All characters.
OWASP-Compliant XSS Sanitization
Specifically targets and neutralizes dangerous script injection and attribute escape vectors.
100% In-Browser RAM Execution
Zero network transmission. Your proprietary source code, internal templates, and user data remain completely private.
1-Click Copy & Text Download
Instantly copy formatted results to your clipboard or download clean text files for project integration.
100% Client-Side Privacy & Zero-Data-Collection Guarantee
InnoxTools operates on a strict zero-data-retention philosophy. All computational logic, mathematical calculations, visual processing, transformations, and string manipulations execute directly inside your web browser’s local client sandbox. Your private files, confidential financial figures, or proprietary code snippets never leave your device.