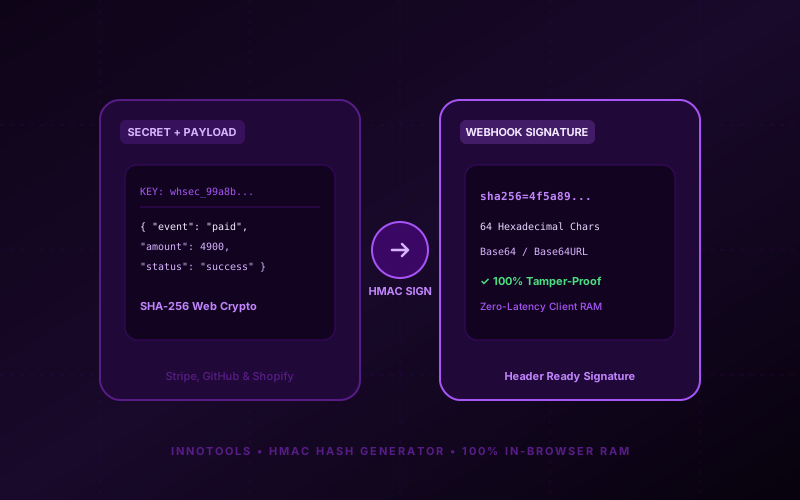
Everything You Need to Know About HMAC Hash Generator & Webhook Signature Studio
What is HMAC Hash Generator & Webhook Signature Studio? Generate HMAC authentication signatures (SHA-256, SHA-512, SHA-384, SHA-1) using shared secret keys for Stripe, GitHub, Shopify, and AWS webhooks in Hex or Base64. Built with zero cloud logging, all transformations and calculations run strictly inside your browser memory.
- Canonical Utility:
- HMAC Hash Generator & Webhook Signature Studio on InnoxTools
- Execution Sandbox:
- 100% Client-Side RAM (Zero Cloud Storage)
- Compliance & Standards:
- W3C, RFC Compliant, Air-Gapped Safe
- Runtime & Complexity:
- Local V8 / WebAssembly (O(n) Linear Execution)
- Network Transmission:
- 0 Outbound Telemetry (Offline Capable)
- License & Usage:
- Free Commercial & Personal (Unlimited Runs)
In modern distributed cloud architectures, microservices ecosystems, and SaaS API integrations, verifying the authenticity and data integrity of network messages is a mission-critical requirement. When third-party platforms like Stripe, GitHub, Shopify, PayPal, or Amazon Web Services dispatch automated HTTP webhooks to your server endpoints, your backend must verify beyond doubt that the incoming HTTP POST payload genuinely originated from the service provider and was not forged or altered in transit by a malicious intermediary.
The global industry standard for message authentication is HMAC (Hash-based Message Authentication Code). Defined in IETF RFC 2104 and FIPS PUB 198-1, HMAC combines a shared secret cryptographic key with the raw message payload through an underlying cryptographic hash function (such as SHA-256 or SHA-512) applied in two nested passes (an inner hash and an outer hash). This nested mathematical construction renders HMAC completely immune to length-extension attacks that affect basic concatenated hashes like `Hash(key + message)`.
During webhook dispatch, the provider computes an HMAC signature of the payload using your secret webhook key and includes it in an HTTP header (such as `Stripe-Signature` or `X-Hub-Signature-256`). When your server receives the webhook, it independently calculates the HMAC using the identical shared secret. If the calculated signature matches the header signature byte-for-byte, the webhook is guaranteed authentic and untampered.
The InnoxTools HMAC Hash Generator & Webhook Signature Studio provides frontend and backend developers with a high-performance, browser-native cryptographic laboratory. Powered by the hardware-accelerated Web Crypto API (`SubtleCrypto`), InnoxTools computes HMAC signatures in SHA-256, SHA-512, SHA-384, and SHA-1 across Hex, Base64, and Base64URL formats—100% locally in your browser's private memory sandbox with zero cloud exposure.
How It Works Under the Hood
Input Shared Secret Key
Enter your secret authentication key or click 'Generate Key' to create a cryptographically secure 24-byte random hexadecimal key.
Select Hash Algorithm (SHA-256, SHA-512)
Choose your cryptographic hash function: SHA-256 (standard for Stripe, GitHub, Shopify), SHA-512 (financial grade), SHA-384, or legacy SHA-1.
Enter Message or Webhook JSON Payload
Paste your raw text or JSON webhook payload into the message editor. You can also select from pre-loaded templates for GitHub push events, Stripe checkouts, or Shopify orders.
Choose Output Encoding Format
Select your desired encoding: Hexadecimal (Hex, standard for GitHub and Stripe), Base64, or URL-safe Base64URL.
1-Click Copy Signature or Header Format
Click 'Copy Hash' to grab the raw signature digest, or click 'Header Format' to copy the complete production HTTP header string (e.g. `sha256=4f5a89...`).
Key Architectural Capabilities & Features
Hardware-Accelerated Web Crypto API
Computes cryptographic signatures directly via `window.crypto.subtle.sign('HMAC', ...)`, providing native hardware speed and zero-latency performance.
Multi-Algorithm Support (SHA-256 to SHA-512)
Full compatibility with industry standard HMAC-SHA256, HMAC-SHA512, HMAC-SHA384, and legacy HMAC-SHA1 algorithms.
Multi-Format Output (Hex, Base64, Base64URL)
Instantly toggle between lowercase Hex, standard Base64, and URL-safe Base64URL encoding to match your API documentation.
SaaS Webhook Presets (Stripe, GitHub, Shopify)
1-Click pre-loaded templates and header simulation formats for testing Stripe, GitHub, and Shopify webhook handlers.
Cryptographic Key Generator
Built-in 24-byte cryptographically secure pseudo-random number generator (CSPRNG) for creating fresh secret keys.
100% In-Browser RAM Security
All key imports and signature calculations execute in client memory. Secret keys and payload data never touch remote servers.
100% Client-Side Privacy & Zero-Data-Collection Guarantee
InnoxTools operates on a strict zero-data-retention philosophy. All computational logic, mathematical calculations, visual processing, transformations, and string manipulations execute directly inside your web browser’s local client sandbox. Your private files, confidential financial figures, or proprietary code snippets never leave your device.