Everything You Need to Know About Bcrypt Hash Generator & Password Verifier
What is Bcrypt Hash Generator & Password Verifier? Generate secure, salted Bcrypt password hashes ($2a, $2b) with customizable cost rounds (4-14) and verify candidate passwords against existing hashes with 100% in-browser RAM security. Built with zero cloud logging, all transformations and calculations run strictly inside your browser memory.
- Canonical Utility:
- Bcrypt Hash Generator & Password Verifier on InnoxTools
- Execution Sandbox:
- 100% Client-Side RAM (Zero Cloud Storage)
- Compliance & Standards:
- W3C, RFC Compliant, Air-Gapped Safe
- Runtime & Complexity:
- Local V8 / WebAssembly (O(n) Linear Execution)
- Network Transmission:
- 0 Outbound Telemetry (Offline Capable)
- License & Usage:
- Free Commercial & Personal (Unlimited Runs)
In modern information security, storing user passwords in plaintext or using outdated cryptographic algorithms like MD5 or SHA-1 is a catastrophic vulnerability. Fast general-purpose hashing algorithms were designed for file checksum verification, allowing modern graphics processing units (GPUs) and application-specific integrated circuits (ASICs) to compute billions of hashes per second—enabling attackers to crack leaked password databases within minutes using precomputed rainbow tables.
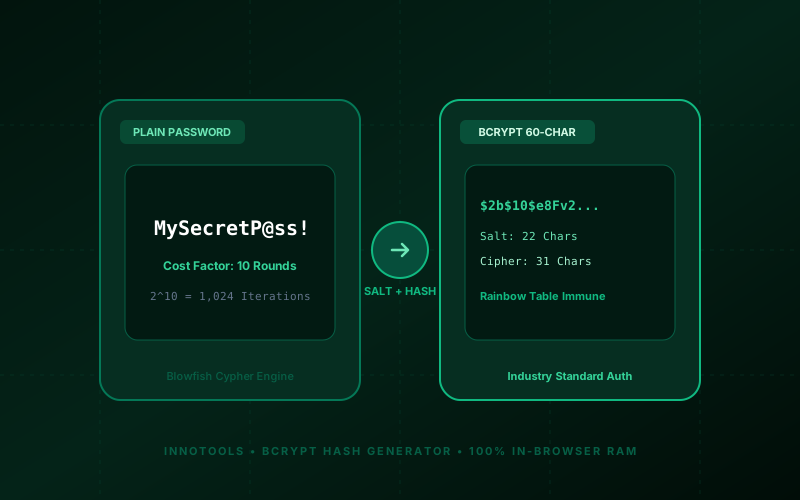
To counter this vulnerability, Niels Provos and David Mazières designed Bcrypt in 1999 based on Bruce Schneier's Blowfish cipher. Bcrypt was intentionally engineered to be computationally expensive and memory-intensive, featuring an adaptive work factor (salt rounds). Each increment of the cost parameter doubles the computational effort required to hash a password (`2^cost`), ensuring that as consumer computing power advances over decades, system administrators can simply increase the iteration cost to keep passwords secure.
A standard Bcrypt hash is a compact 60-character string comprising four distinct components: the algorithm version identifier (such as `$2a$` or `$2b$`), the cost factor (such as `10`, representing `2^10 = 1,024` rounds), a randomly generated 128-bit salt encoded in 22 Radix-64 characters, and a 184-bit ciphertext checksum (31 characters). Because a unique cryptographic salt is generated for every individual password, two users with identical passwords will always produce completely distinct, uncrackable hashes.
The InnoxTools Bcrypt Hash Generator & Password Verifier brings military-grade password hashing and verification directly into your web browser. Engineered by INNO XPERT, our client-side cryptographic engine operates 100% locally in your browser's private RAM sandbox. Whether you are generating test database seeds, configuring Docker environment variables, or auditing user password verification logic, InnoxTools delivers instantaneous results with zero cloud exposure, complete confidential privacy, and live execution benchmarking.
How It Works Under the Hood
Input Plaintext Password
Type or paste your password string into the plaintext input field. Use the visibility toggle to show or hide sensitive characters.
Adjust Salt Rounds (Cost Factor)
Use the slider to select your desired cost factor from 4 (rapid testing) to 14 (maximum production security). The default 10 rounds represents 1,024 iterations.
Generate Salt & Hash in Client RAM
Click 'Generate Fresh Hash' to compute the cryptographic salt and ciphertext checksum locally on your device's CPU.
Inspect Hash Anatomy & Latency
Review the decomposed hash anatomy breakdown: algorithm prefix ($2b$), cost factor ($10$), 22-character salt, 31-character checksum, and real-time execution latency in milliseconds.
Verify Candidate Password Matches
Switch to the 'Verify Password' tab to test whether a candidate plain password matches an existing stored hash with instant green/red verification feedback.
Key Architectural Capabilities & Features
100% In-Browser Local RAM Execution
All salt generation, key expansion, and Blowfish cipher rounds execute on your client device. Zero passwords or hashes are transmitted across the internet.
Adaptive Cost Rounds Calibration (4-14)
Freely calibrate iteration intensity from 4 rounds (dev testing) up to 14 rounds (16,384 iterations) with live benchmark timing.
Dual Mode (Generate & Match Verifier)
Generate fresh salted hashes or test existing database hashes against plaintext candidate passwords in one unified utility.
Deconstructed Hash Anatomy Visualizer
Clearly separates and explains the algorithm identifier ($2b$), cost parameter ($10$), 22-character salt, and 31-character checksum.
Anti-Rainbow Table Salt Protection
Generates authentic 128-bit cryptographically secure random salts for every single execution, preventing dictionary and precomputed lookup attacks.
1-Click Clipboard & Seed Export
Instantly copy generated 60-character hashes for pasting into SQL database migrations, Docker `.env` files, or test suites.
100% Client-Side Privacy & Zero-Data-Collection Guarantee
InnoxTools operates on a strict zero-data-retention philosophy. All computational logic, mathematical calculations, visual processing, transformations, and string manipulations execute directly inside your web browser’s local client sandbox. Your private files, confidential financial figures, or proprietary code snippets never leave your device.