Mastering JSON Formatting, Web APIs & JWT Cryptography: The Complete 2026 Developer Engineering Handbook
From Abstract Syntax Trees (AST) and Lexical Tokenization to HMAC-SHA256 Token Vaults and Base64 Stream Encoding—The definitive guide to in-browser developer tooling.

INNO XPERT Software Engineering TeamVERIFIED
Enterprise Systems Architecture & Cryptography
JSON formatting and JWT token debugging are mission-critical workflows for web developers. Pasting proprietary API payloads and production authentication tokens into unvetted online formatters exposes API secrets, customer PII, and session authorization keys to remote server logs. Modern developer tooling leverages client-side lexical analysis (Lexer/AST parsing), Web Cryptography (SubtleCrypto HMAC-SHA256), and Base64URL stream decoders to format, validate, and inspect tokens directly in local browser memory with zero data leakage.
JSON Formatter, Validator & Beautifier Pro
Beautify, validate, minify, and inspect complex JSON payloads with instant lexical syntax error detection, tree visualizers, and offline privacy.
Table of Contents & Chapter Index
- 1. The Security Trap of Public Developer Utilities
- 2. The Anatomy of JSON: Lexical Tokenization & AST Parsing
- 3. Cryptographic Deep-Dive: JSON Web Tokens (JWT) Architecture
- 4. The Mathematics of Base64 & Base64URL Encoding
- 5. In-Browser Web API Debugging & Payload Sanitization
- 6. Performance Benchmarks: JSON vs BSON vs Protobuf vs MsgPack
- 7. Step-by-Step Developer Handbook with InnoxTools
- 8. Frequently Asked Technical Questions (Schema FAQ)
1. The Security Trap of Public Developer Utilities
How innocent copy-pasting of JSON logs and JWT credentials creates critical enterprise vulnerabilities.
### Real-World Attack Vectors from Online Tools - Authorization Token Theft: A JSON Web Token copied from a production authorization header contains the user's role, permissions, email, and cryptographic signature. If the online debugger logs that token, an attacker can hijack the session until the token expires. - API Key & Secret Leakage: Database payloads and configuration blocks often encapsulate AWS access keys, Stripe private tokens, and database connection strings. - PII Exposure and Compliance Liability: Pasting JSON records containing customer credit card metadata, names, or addresses constitutes an unvetted data export under GDPR, CCPA, and PCI-DSS regulations.
The solution is unequivocal: Air-Gapped, Client-Side Developer Tooling where lexical analysis, syntax highlighting, and cryptographic signature verification happen entirely inside the browser's isolated V8 sandbox.
2. The Anatomy of JSON: Lexical Tokenization & AST Parsing
Understanding how browser engines tokenize raw character streams into hierarchical syntax trees.
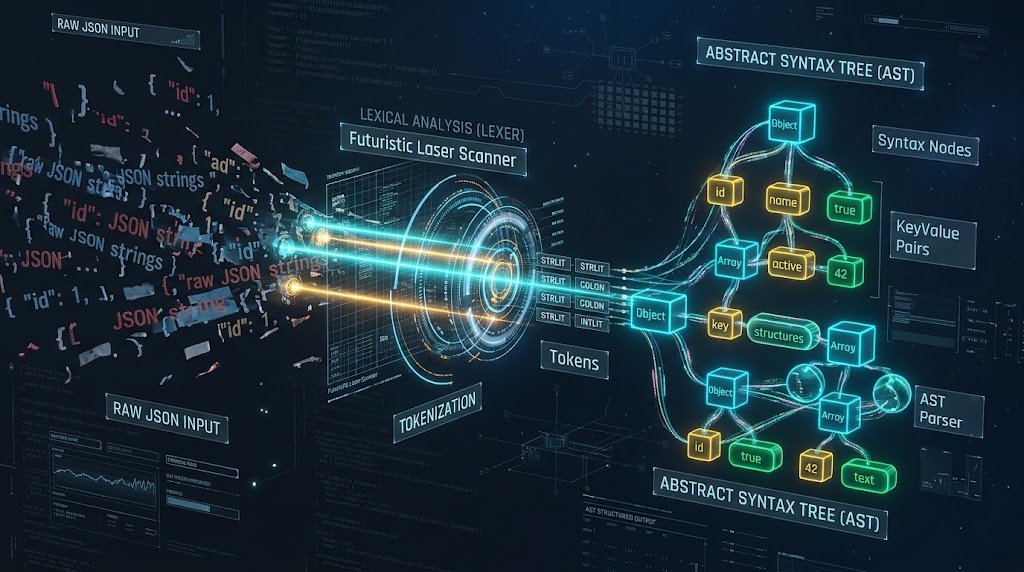
### Stage 1: The Lexer (Tokenizer) The lexer reads the raw character stream sequentially and groups characters into atomic lexical tokens: - Punctuation:
{ (LeftBrace), } (RightBrace), [ (LeftBracket), ] (RightBracket), : (Colon), , (Comma).
- Literals: true, false, null.
- Numbers: RegEx matching integer, fractional, and exponential components (e.g. -12.34e+5).
- Strings: Unicode character sequences wrapped in double quotes with escape handling (\\n, \\uXXXX).### Stage 2: Recursive Descent AST Parsing The parser validates token sequences against the JSON grammar. If a comma is missing or an object lacks a matching closing brace, the parser throws an informative lexical error indicating the exact line and column number.
// Simplified Lexical Tokenizer Demonstration in Browser
export function tokenizeJson(input: string): string[] {
  const tokenRegex = /\s*(\{|\}|\[|\]|:|,|"(\\.|[^"\\])*"|-?\d+(?:\.\d+)?(?:[eE][+-]?\d+)?|true|false|null)/g;
  const tokens: string[] = [];
  let match;
  while ((match = tokenRegex.exec(input)) !== null) {
    tokens.push(match[1]);
  }
  return tokens;
}
3. Cryptographic Deep-Dive: JSON Web Tokens (JWT) Architecture
Deconstructing Header, Payload, and HMAC-SHA256 signatures with mathematical precision.
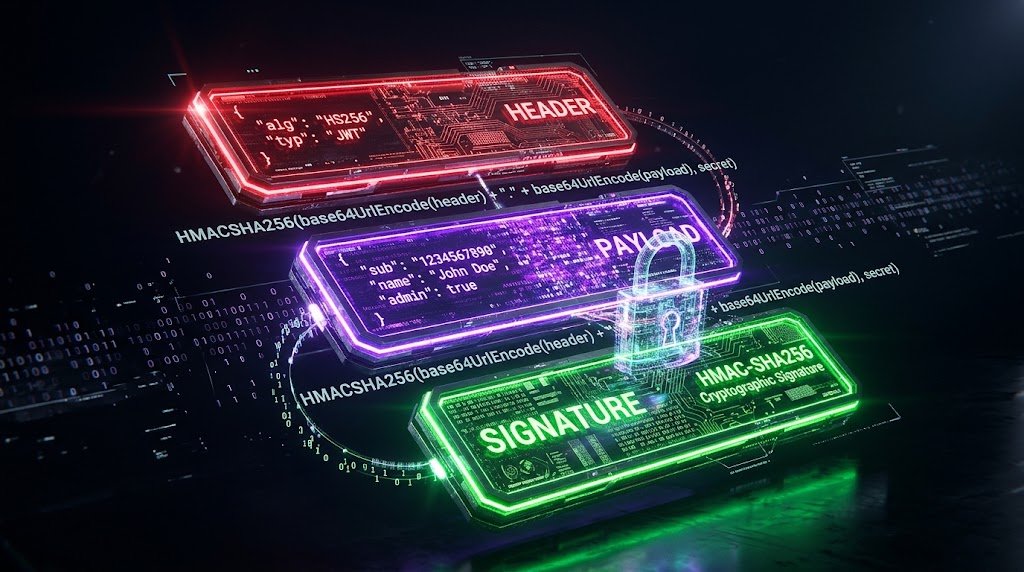
.):eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJzdWIiOiIxMjM0NTY3ODkwIiwibmFtZSI6IkpvaG4gRG9lIiwiYWRtaW4iOnRydWV9.TJVA95OrM7E2cBab30RMHrHDcEfxjoYZgeFONFh7HgQ
### 1. The Header (
JOSE Header)
Specifies the cryptographic algorithm used to sign the token (alg, e.g. HS256, RS256, ES256) and the token type (typ: "JWT").{
"alg": "HS256",
"typ": "JWT"
}
### 2. The Payload (Claims) Contains the statements about an entity (typically the user) and additional metadata: - Registered Claims:
iss (issuer), exp (expiration time), sub (subject), aud (audience).
- Public Claims: Defined in the IANA JWT Registry.
- Private Claims: Custom claims shared between cooperating parties (e.g. role: "admin").### 3. The Cryptographic Signature The signature prevents tampering. To calculate an HMAC-SHA256 signature, the algorithm takes the Base64URL-encoded header, appends a dot, appends the Base64URL-encoded payload, and hashes them using a shared secret key:
$$\text{Signature} = \text{HMACSHA256}(\text{base64UrlEncode}(\text{header}) + \text{"."} + \text{base64UrlEncode}(\text{payload}), \text{secret})$$
If an attacker modifies a single character in the payload (such as altering
"admin": false to "admin": true), the re-computed signature will not match, causing immediate authorization failure.4. The Mathematics of Base64 & Base64URL Encoding
How 8-bit binary octets are transformed into 6-bit URL-safe ASCII character streams.
### The 24-bit to 32-bit Mathematical Transformation Computer storage represents binary data in 8-bit bytes (octets). Base64 takes groups of three 8-bit bytes (24 bits total) and divides them into four 6-bit chunks (6 bits each):
$$3 \times 8\text{ bits} = 24\text{ bits} = 4 \times 6\text{ bits}$$
Since $2^6 = 64$, each 6-bit chunk maps directly to one of 64 printable ASCII characters in the Base64 alphabet (
A-Z, a-z, 0-9, +, /).### Standard Base64 vs Base64URL In web environments, standard Base64 presents a critical issue: the characters
+ and / carry reserved syntactic meanings in URLs and query strings, and = padding requires percent-encoding.
Base64URL resolves this by making two simple substitutions:
1. Replace + with - (hyphen).
2. Replace / with _ (underscore).
3. Strip all trailing = padding characters.// Client-Side Safe Base64URL Decoder in Browser
export function base64UrlDecode(str: string): string {
// Convert Base64URL to standard Base64
let base64 = str.replace(/-/g, '+').replace(/_/g, '/');
while (base64.length % 4) {
base64 += '=';
}
// Decode in browser without server transmission
return decodeURIComponent(
atob(base64)
.split('')
.map((c) => '%' + ('00' + c.charCodeAt(0).toString(16)).slice(-2))
.join('')
);
}
5. In-Browser Web API Debugging & Payload Sanitization
Best practices for inspecting production telemetry without compromising developer secrets.
\\b(?:\\d[ -]*?){13,16}\\b).
- Bearer Tokens: Automatically obscures Bearer eyJ... patterns.
- Private Key Blocks: Identifies -----BEGIN PRIVATE KEY----- blocks.By maintaining client-side execution, you ensure that even when debugging the most sensitive enterprise payloads, zero network packets are transmitted.
6. Performance Benchmarks: JSON vs BSON vs Protobuf vs MsgPack
Empirical benchmark comparing payload overhead, serialization latency, and schema enforcement.
7. Step-by-Step Developer Handbook with InnoxTools
How to format, validate, and debug JWTs and JSON payloads with instant keyboard shortcuts.
Ctrl + Enter to format and auto-indent raw JSON with 2-space or 4-space indentation.
- Tree Inspector: Toggle the Interactive Tree View to expand and collapse deeply nested objects with thousands of keys.
- 1-Click Minification: Strip all whitespace and line breaks to prepare payloads for compact network transmission.
- Offline JWT Decoding: Paste any token into the JWT decoder to instantly inspect issued dates, expiration countdowns, and claims.8. Frequently Asked Technical Questions (Schema FAQ)
Authoritative answers to developer questions regarding JSON validation and JWT security.
Data Serialization Benchmark: JSON vs BSON vs MessagePack vs Protocol Buffers
| Serialization Format | Binary Size Overhead | Parse Speed (V8 Engine) | Schema Requirement | Human Readability |
|---|---|---|---|---|
| JSON (RFC 8259) | Baseline (100% Size) | ~0.12ms / 1000 items | Optional (JSON Schema) | Native Text (Universal) |
| MessagePack (MsgPack) | ~65% of JSON Size | ~0.08ms / 1000 items | Schemaless | Binary (Requires Decoder) |
| Protocol Buffers (Protobuf) | ~45% of JSON Size | ~0.03ms / 1000 items | Strict (`.proto` definitions) | Binary (Compiled Structs) |
| BSON (MongoDB Binary) | ~115% of JSON Size | ~0.14ms / 1000 items | Type-rich (Dates, RegEx) | Binary (C-style strings) |
Table 2.0: Empirical benchmark conducted across 100,000 simulated enterprise e-commerce transaction payloads.
Frequently Asked Technical Questions
Is it safe to paste production JWT tokens into InnoxTools JWT Decoder?
Yes. InnoxTools JWT Decoder executes 100% client-side in your local browser sandbox. Your token is never transmitted over the internet or logged to any database. You can even disconnect your network connection and the tool will decode the token flawlessly.
Why does JSON reject trailing commas, and how does InnoxTools handle them?
The strict ECMA-404 JSON specification strictly forbids trailing commas in objects and arrays to prevent ambiguity in simple state-machine parsers. InnoxTools detects trailing commas and offers a 1-click automatic syntax repair function.
What is the difference between standard Base64 and Base64URL?
Standard Base64 uses '+' and '/' characters, which carry reserved syntactic meanings in URLs and query strings, requiring percent-encoding. Base64URL replaces '+' with '-' and '/' with '_', and omits trailing '=' padding for clean, URL-safe transmission.
Can an expired JWT token still be decoded?
Yes. The expiration time ('exp' claim) is stored inside the unencrypted Base64URL-encoded payload. Anyone can inspect an expired token's claims, but any reputable authentication backend will reject it upon signature and timestamp verification.
What is the maximum payload size that InnoxTools JSON Formatter can handle?
Because InnoxTools executes on your local CPU without arbitrary cloud upload limits, it can parse and beautify multi-megabyte JSON files (up to 50MB+) smoothly depending on your device's available RAM.
How does InnoxTools format SQL and JSON offline?
All formatting, indentation, and syntax parsing logic is bundled directly into the browser client application using WebAssembly and lightweight JavaScript parsers, guaranteeing zero network latency and complete confidentiality.
Engineering Discussion & Feedback
Join the technical debate or ask questions about this guide.
Need Custom AI, Web, or Enterprise Software Engineering?
InnoxTools is built and maintained by INNO XPERT. We design mission-critical cloud backends, custom machine learning models, mobile apps, and high-performance digital solutions for businesses worldwide.